From Vulnerability Scanning to Remediation: How to Decide What to Fix First
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
Our products
The compliance platform built by our cybersecurity practice. Its built-in AI automates the gap analysis for NIS2 and the Czech Cybersecurity Act.
Cybersecurity
Discover why outsourcing a CISO and cybersecurity specialists pays off for companies. Flexibility, cost savings, and faster preparation for NIS2.
The number of cyberattacks and threats is growing every day, and serious vulnerabilities are being discovered even in the systems of the largest IT service providers. In Europe, the NIS2 Directive now applies, in Czechia through the Cybersecurity Act, requiring companies to establish systems that reliably protect their infrastructure and data. Yet, there is a shortage of qualified professionals with relevant experience. Recruiting and retaining them is both complex and financially demanding. For this reason, more and more organisations are choosing to outsource a CISO (Chief Information Security Officer) as well as other cybersecurity specialists.
The CISO is responsible for the overall cybersecurity strategy of the organisation. They ensure compliance with regulations, establish processes, and oversee the company’s ability to respond quickly to incidents. Their role covers implementing technical measures, managing security processes and maintaining regular communication with executive leadership.
An external CISO and a team of specialists bring several advantages. The first is access to experts with experience across different industries. While hiring a full-time CISO may be financially unfeasible for small and medium-sized companies, outsourcing offers a flexible model: organisations pay only for the services they need.
Another advantage is eliminating the inefficiency of a full-time role. In many companies, the CISO’s agenda is not extensive enough to justify the high cost of a senior professional on a permanent contract. Outsourcing helps avoid overpaying for an underutilised employee. Instead, the company gains optimal capacity based on current needs: for example, intensive support from a specialist during audit preparation, followed by periodic oversight and reporting.
A further benefit is faster onboarding. Recruitment and hiring of qualified employees can take months, while external capacity can be engaged much sooner. Outsourcing also provides an objective outside perspective, helping to uncover weaknesses that an internal team might overlook.
In addition to outsourcing the CISO role itself, companies often turn to staff augmentation, reinforcing their teams with specialists based on current needs. This allows organisations to bring in an auditor, a security systems architect, a supplier risk management specialist, or an incident response expert. Common scenarios include preparing for an audit, implementing NIS2, or achieving ISO 27001 certification. In these cases, external support accelerates the process and minimises the risk of errors.
Consider a mid-sized energy company subject to the NIS2 directive. Internally, it lacks the capacity and expertise to handle complex cybersecurity regulations. By outsourcing a CISO and engaging an external team, the company can conduct a gap analysis, prepare the necessary documentation, and establish risk management processes. To support these efforts, we developed AuditMaster.ai, an AI-powered tool that simplifies the whole process of complying with current legislation. As a result, the company can meet its obligations on time, without chaos, and at a lower cost than building a full in-house department.
Outsourcing delivers significant benefits, but it requires careful partner selection. An external CISO must not only have technical expertise but also a strong understanding of regulations and the ability to communicate effectively with company leadership. Confidentiality, clearly defined SLAs, and transparent reporting are essential. Only under these conditions will outsourcing serve as real support rather than a new source of risk.
Outsourcing a CISO and cybersecurity specialists is a response to today’s labour market challenges and stricter regulatory requirements. It offers companies flexibility, access to expertise, and cost savings. For organisations that are preparing for NIS2 or aiming to strengthen their resilience against threats, outsourcing is often the quickest way to bring that expertise on board.
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
What should you prepare in the first year after registering a regulated service? A ZoKB checklist covering risks, security measures, incidents and recovery.
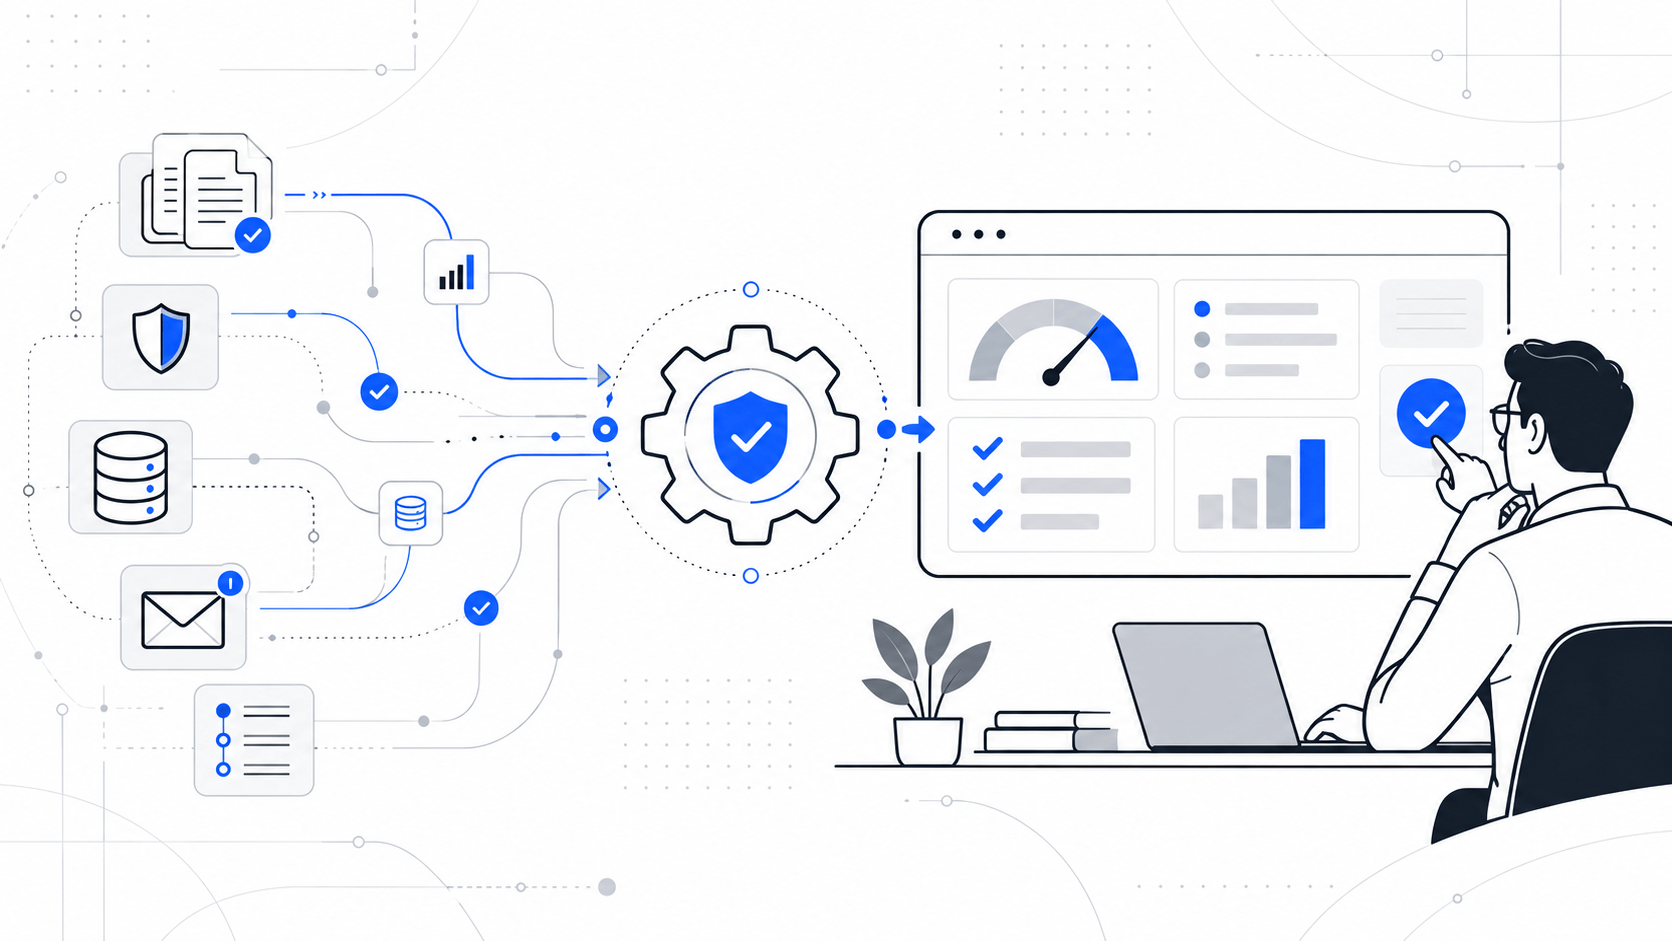
Learn which GRC activities can be automated, where AI adds value, and why evidence, control and risk decisions still require expert human judgement.
Tell us what you need to secure, automate, build or staff. A senior consultant will get back to you.
 Aleš PoláčekCEO, Whirr Crew
Whirr Crew s.r.o., Rybná 716/24, 110 00 Praha 1