From Vulnerability Scanning to Remediation: How to Decide What to Fix First
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
Our products
The compliance platform built by our cybersecurity practice. Its built-in AI automates the gap analysis for NIS2 and the Czech Cybersecurity Act.
Cybersecurity
What determines how long NIS2 implementation takes, why it can't be rushed, which Czech deadlines apply now and how Whirr Crew helps.
You probably know the feeling – everyone in the company has their own priorities. Operations, customers, deliveries, finance. Somewhere between all that and the IT department, cybersecurity should also have its place. Cyberattacks are a daily reality, while business moves fast and there are always too many priorities. If you sense that preparing for NIS2 won't become a priority anytime soon, at least take a few minutes to read about what the consequences could be.
Postponing the work on new regulations could be the most expensive mistake your company makes. Implementing security measures in line with NIS2 doesn't happen overnight. It requires a plan, resources and above all time, and in Czechia the legal deadlines are already running.
How long implementation takes depends on the size of the organisation, the current level of its security management and its technical infrastructure. It is a matter of months, and for larger or more complex organisations it takes longer still.
The entire process begins with mapping the initial state – without this, a proper gap analysis cannot be conducted. This gap assessment reveals the areas that need attention during implementation. In addition to rolling out technical security measures, it's essential to document your processes and keep clear records of company assets, risks, suppliers, employee training history and much more.
Now, let's be honest – how many of these steps could your team realistically complete in just three months?
Experienced cybersecurity professionals are hard to find. If your internal resources are limited, you may quickly run into trouble. A CISO (Chief Information Security Officer) who understands both business and the specific demands of NIS2 is a rare find today. The later a company starts, the smaller its chances of securing the expertise it needs.
This is exactly why Whirr Crew offers CISO outsourcing. Through this model, companies gain access to a senior cybersecurity manager who can define a security strategy, oversee the security management system and prepare the company for audits, without the need to expand the internal team.
Cybersecurity success isn't about "having some documents in the cloud." It's about knowing what you're doing, why you're doing it, and proving that it works. In many organisations, implementing NIS2 requires new processes, assigned responsibilities and proper employee training. There's a lot to be done, and time won't wait.
At Whirr Crew, we follow the proven Plan – Do – Check – Act (PDCA) approach to managing cybersecurity effectively:
Cybersecurity isn't a one-time project. It's a system of processes that must become part of your company's day-to-day operations. That's the only way to ensure long-term, effective protection against threats.
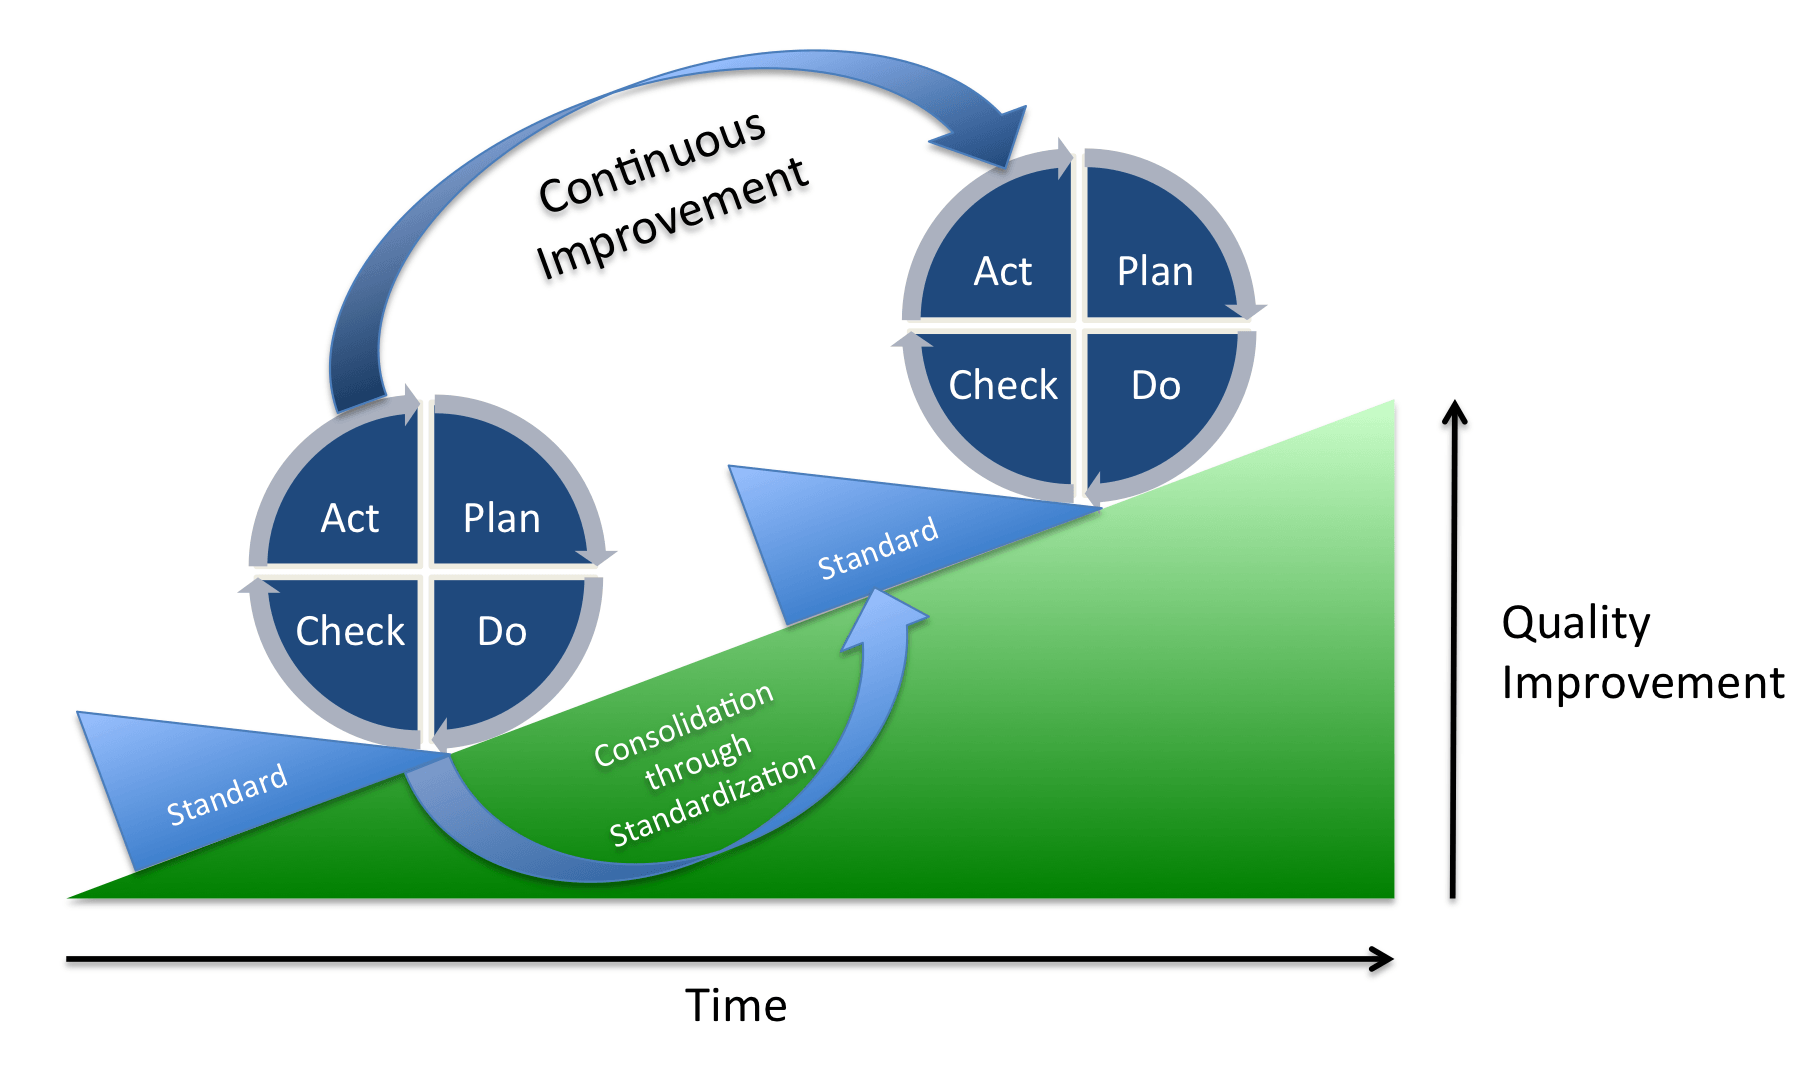
Depiction of the PDCA cycle (also known as the Deming cycle). Continuous quality improvement is achieved by iteratively moving through the cycle and reinforcing progress through standardisation. | Johannes Vietze
The new cybersecurity legislation in the Czech Republic, Act No. 264/2025 Coll., has been in force since 1 November 2025.
Its deadlines are not about "changes to implement one day", but about concrete obligations that run from specific dates. These are the key steps.
An organisation providing a regulated service must notify it to the National Cyber and Information Security Agency (NÚKIB). For organisations that met the conditions when the Act took effect, the deadline was 31 December 2025; if you missed it, notify now. NÚKIB then delivers a decision on registration, and from that day you are a provider of a regulated service.
Within 30 days of delivery of the decision, the organisation reports the contact details of the people authorised to act for it in cybersecurity matters, together with supplementary data about the service.
Within one year of delivery of the decision, the organisation must:
From then on, NÚKIB can check how the organisation meets these obligations. If your decision arrived around the turn of 2025 and 2026, your one-year deadline falls around the turn of 2026 and 2027. What to complete in that year is in our ZoKB checklist.
NIS2 is not just another bureaucratic obligation. It is an opportunity to finally set up cybersecurity in a way that makes real sense from a business, operational and strategic perspective. Those who start now give themselves the best chance of meeting the one-year deadline.
Schedule a consultation with Whirr Crew.
We'll help you create a realistic plan and implement NIS2 in a way that fits your business.
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
What should you prepare in the first year after registering a regulated service? A ZoKB checklist covering risks, security measures, incidents and recovery.
Learn which GRC activities can be automated, where AI adds value, and why evidence, control and risk decisions still require expert human judgement.
Tell us what you need to secure, automate, build or staff. A senior consultant will get back to you.
 Aleš PoláčekCEO, Whirr Crew
Whirr Crew s.r.o., Rybná 716/24, 110 00 Praha 1