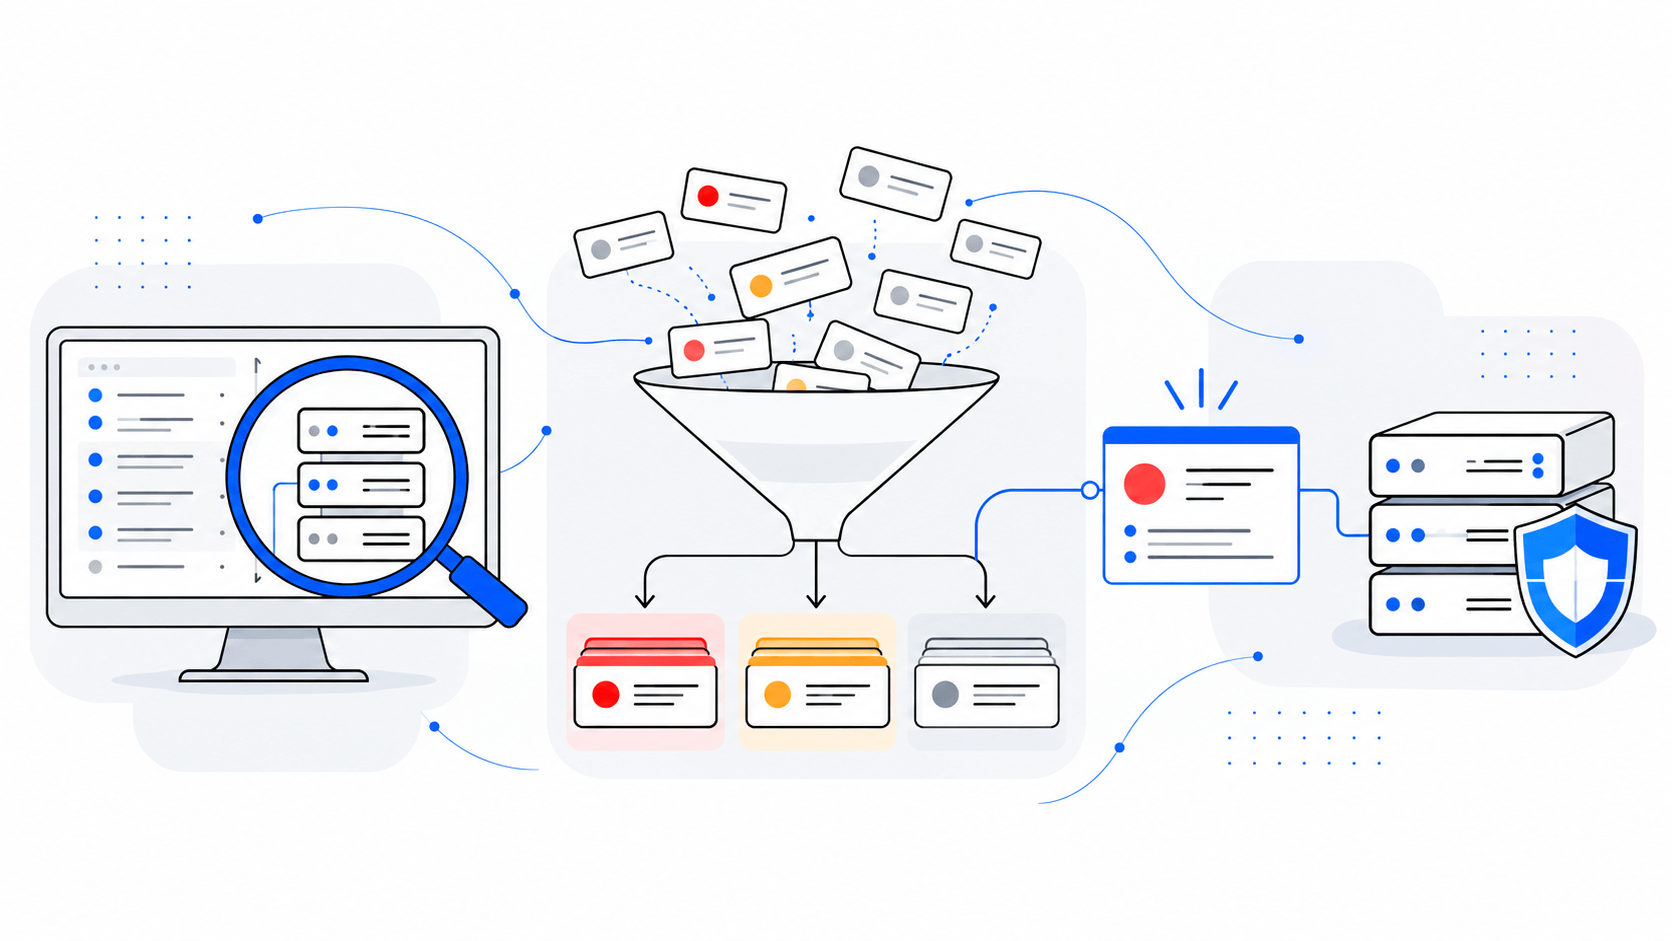
From Vulnerability Scanning to Remediation: How to Decide What to Fix First
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
Our products
The compliance platform built by our cybersecurity practice. Its built-in AI automates the gap analysis for NIS2 and the Czech Cybersecurity Act.
Cybersecurity
Not sure where to begin with NIS2 implementation? We’ll guide you through creating a step-by-step plan even without an internal security team.
The European NIS2 Directive brings cybersecurity obligations that affect thousands of Czech companies. If your organisation falls into the category of “regulated entities”, you are required to adopt technical and organisational measures, maintain a supplier registry, provide employee training, and be prepared for audits, all within a relatively short timeframe.
The good news is that achieving NIS2 compliance doesn’t necessarily mean building a full internal security team. The key is to have a well-thought-out plan, make smart use of available tools, and break the implementation into manageable steps.
The first step is to confirm whether the new rules actually apply to your business. NIS2 targets companies in critical sectors (such as IT, healthcare, transport, or digital infrastructure) with 50 or more employees, or an annual turnover and balance sheet total both above EUR 10 million. The exact categorisation and scope of obligations are defined in the Czech Cybersecurity Act (ZoKB).
If you’re unsure, you can consult an expert or use online assessment tools that provide a quick evaluation after answering a few basic questions about your company. You can try the AuditMaster.ai questionnaire.
A gap analysis is the foundation of any NIS2 implementation. It compares your current measures with NIS2 requirements and highlights gaps: areas where you need to update documentation, processes, or technical controls. We wrote about gap analyses in an earlier article on gap analysis as the first step toward NIS2 compliance.
While such assessments used to take weeks or even months of consultant work, today AI-powered tools can deliver results in minutes. The outcome is a clear list of missing measures, often with concrete recommendations on how to fix them.
Based on your gap analysis and risk mapping, create a phased plan that prioritises activities according to urgency and available resources. A practical timeline might look like this:
Having such a plan also helps demonstrate your compliance efforts if audited by NÚKIB.
NIS2 addresses more than internal processes: it also emphasises risk management across your supply chain. Even smaller companies need to know who provides their critical services, the risks involved, and the potential impact of disruptions.
Key tasks include:
Tools like AuditMaster.ai make it easier to manage all this information in one place, simplifying audit readiness and ongoing compliance.
One of NIS2’s core requirements is clearly defined accountability for cybersecurity. Prepare key documents such as security policies, training plans, access control policies, and incident response procedures.
Whirr Crew can support you across this area: through consulting, drafting documents for your organisation, or even outsourcing key roles like CISO or security auditor. We also provide ready-to-use templates for security documentation.
Implementation doesn’t stop once the measures are in place. You’ll need to:
Again, AuditMaster.ai helps by managing documentation, tracking obligations, and maintaining evidence for audits.
The key to successful NIS2 implementation is a solid plan, smart use of tools, and effective project leadership. You don’t need a large in-house security team, as long as you have access to the right people and technologies.
At Whirr Crew, we specialise in efficient, sustainable NIS2 compliance. From initial assessments and policy development to long-term support, we help you through the entire process.
Curious how this could work in your organisation?
Decide what to fix first after a vulnerability scan. Prioritise findings by asset criticality, exposure and business risk, then verify remediation.
What should you prepare in the first year after registering a regulated service? A ZoKB checklist covering risks, security measures, incidents and recovery.
Learn which GRC activities can be automated, where AI adds value, and why evidence, control and risk decisions still require expert human judgement.
Tell us what you need to secure, automate, build or staff. A senior consultant will get back to you.
 Aleš PoláčekCEO, Whirr Crew
Whirr Crew s.r.o., Rybná 716/24, 110 00 Praha 1